Case study · AI security & SaaS
Maskflare: building an AI data protection product and the website that sells it.
A B2B security product that lets companies use AI tools such as ChatGPT, Copilot and Claude without leaking personal or confidential data. We built the product and its website.
The brief
Companies want their teams to use AI, but names, card numbers, IBANs and API keys must not reach external AI providers. Maskflare needed a product that detects and masks that data across employees, in-house applications and AI agents, and a website that explains it to security, compliance and IT buyers.
Evidence
Maskflare is live at maskflare.com with a self-serve free trial. The product ships 574 built-in detectors and 47 country packs, and supports SSO and SCIM with Microsoft Entra ID, Okta and Google Workspace, as published on the product site.
Constraints
- One policy has to cover three very different paths: browser AI apps used by staff, company applications calling AI APIs, and AI agents using tools.
- Masking must be reliable for structured identifiers (checksum and format validation) and reversible for API traffic, so real values can return in the answer.
- The buyers are security, compliance and IT teams in regulated sectors such as finance, insurance, healthcare and legal.
Key decisions
- Structured the product and the website around the three ways data reaches AI models: people, apps and agents.
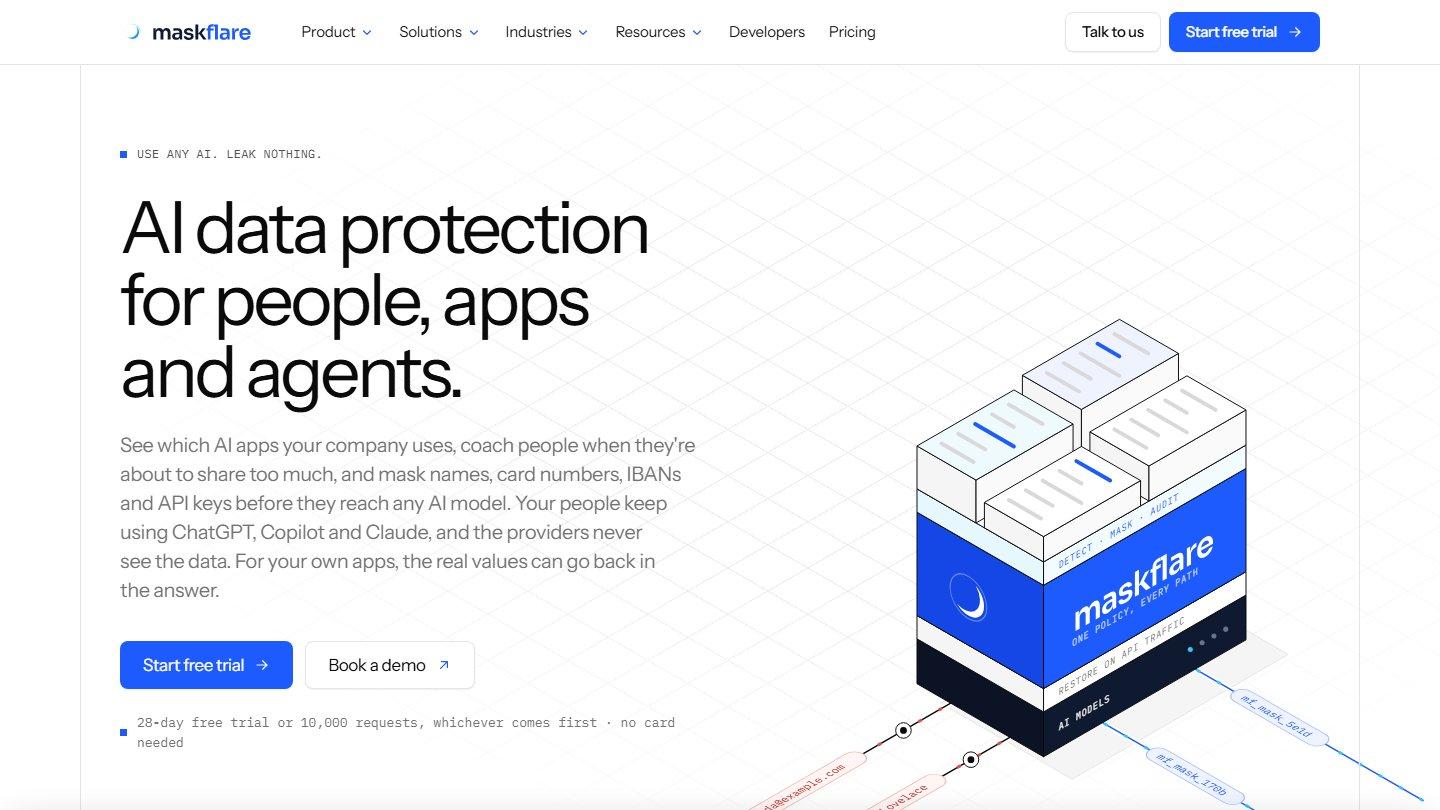
- Led the website with the outcome in plain words, “Use any AI. Leak nothing.”, before technical detail.
- Gave security buyers the facts they check first: detection coverage, data handling, hosting region, SSO/SCIM and audit export.
- Made the free trial (28 days or 10,000 requests, no card) the primary call to action.
Delivered
- SaaS product: masking engine, admin console and integrations
- Product website with industry pages, product tour, FAQ and comparison resources
- Trial and demo conversion paths